Effective DLP Policies for Modern Businesses
Adam Brooks

Introduction
Technology can identify risky files, but technology alone cannot protect sensitive information.
Every successful Data Loss Prevention strategy begins with clear DLP policies that define how information should be handled, what types of data require protection, and how organizations should respond when risks are detected.
For many business owners, the term "DLP policy" sounds highly technical. In reality, effective policies are often simple. They establish practical rules that help employees understand expectations while giving managers visibility into potential risks.
This article explains what DLP policies are, why they matter, and how businesses can create policies that improve security without adding unnecessary complexity.
What Are DLP Policies?
A DLP policy is a set of rules that helps an organization identify and manage sensitive information.
These policies define what types of files require additional attention and what actions should be taken when potential risks are detected.
For example, a company may decide that documents containing customer information, financial data, internal contracts, or confidential reports should receive greater scrutiny than standard business files.
The objective is not to block every possible risk. The objective is to create consistent guidelines that help the organization make better decisions.
Without policies, data protection becomes subjective. Different managers may respond differently to similar situations, creating inconsistency and uncertainty.
With clear policies in place, employees understand expectations and leaders have a framework for evaluating potential risks.
The best policies are practical, understandable, and aligned with how people actually work.
Why Many DLP Policies Fail
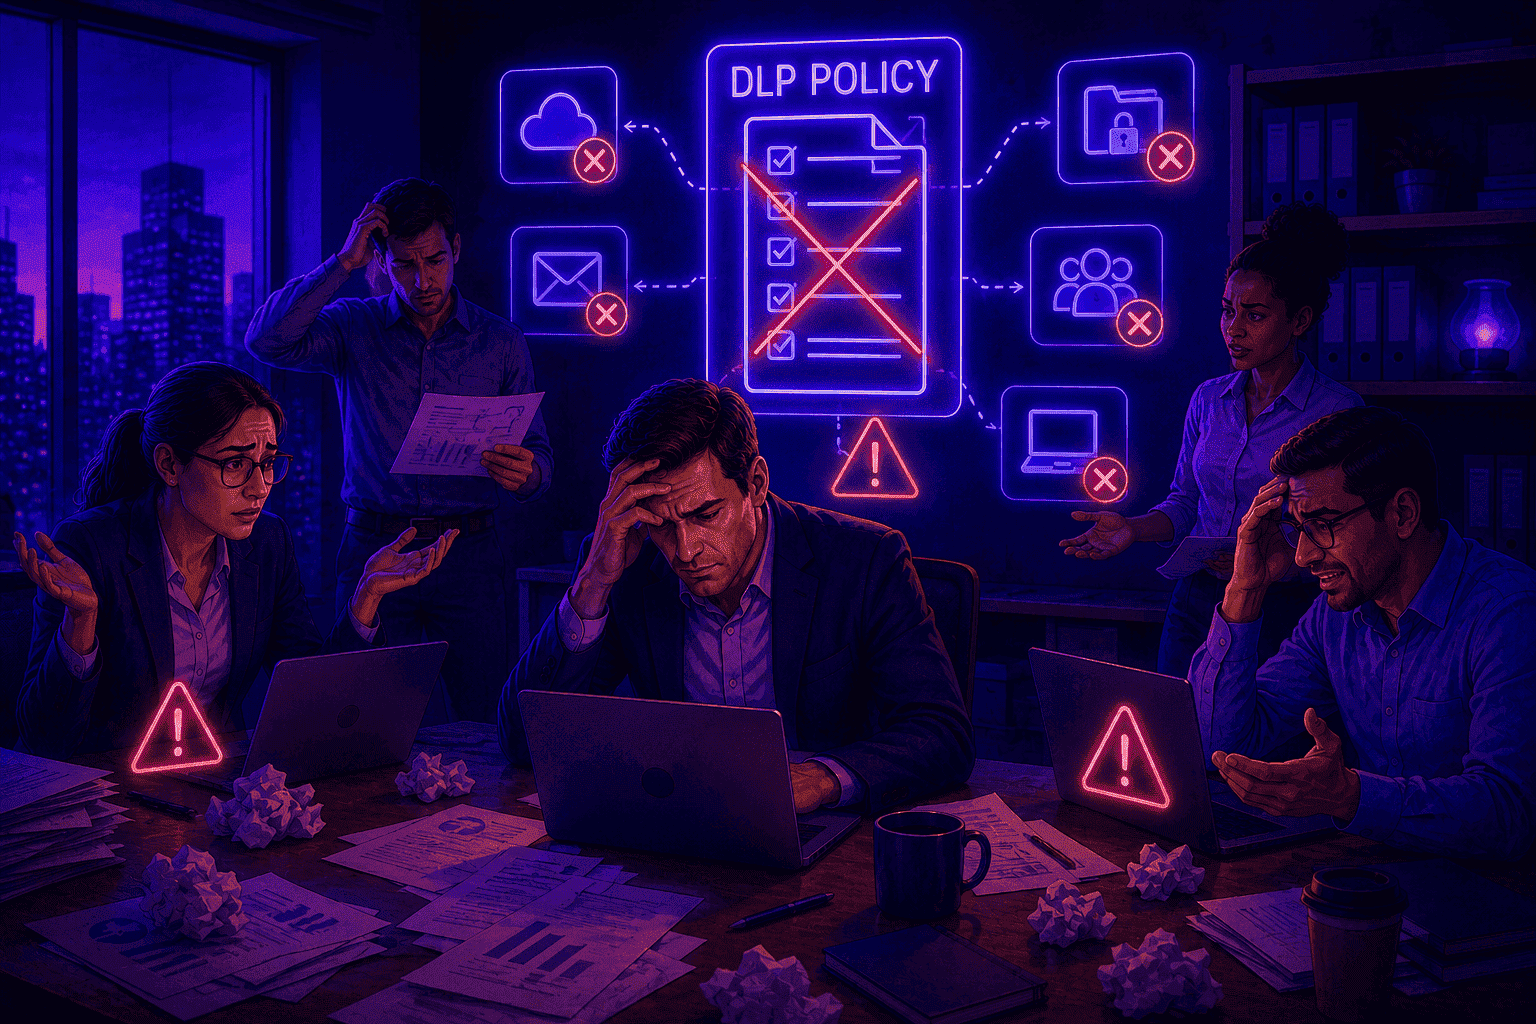
One of the most common mistakes organizations make is creating policies that are too complicated.
When employees cannot understand the rules, compliance decreases.
When managers receive too many alerts, important incidents get overlooked.
Effective DLP policies focus on simplicity.
Instead of creating dozens of categories and exceptions, many businesses achieve better results by concentrating on a few core principles:
Identify Sensitive Information
Determine what information deserves additional protection.
Evaluate Risk
Understand which situations create the greatest exposure.
Review Incidents Consistently
Apply the same process across departments and teams.
A unique challenge is that sensitive information changes over time. As businesses grow, new workflows emerge and new types of information become important.
This is why DLP policies should be reviewed regularly rather than treated as permanent documents.
Using Risk-Based Policies Instead of Complex Rules
Modern DLP solutions are increasingly moving beyond rigid, one-size-fits-all rules. Every organization handles sensitive information differently, which means data protection policies should reflect the specific risks, workflows, and compliance requirements of each business.
Tools such as OrbityTrack allow organizations to define fully customized DLP policies through configurable AI analysis. Instead of relying solely on predefined patterns, businesses can create their own evaluation criteria, prompts, and risk guidelines that align with their internal policies. This enables the system to analyze files according to what the organization considers sensitive, automatically assigning a Risk Index, Risk Range, and justification based on those custom rules.
As a result, DLP becomes more relevant to the organization's reality, reducing false positives and helping managers focus on the incidents that truly matter.
Turning DLP Policies Into Daily Practices
Policies only work when they become part of everyday operations.
Many organizations write policies once and rarely revisit them. As a result, employees forget them and managers stop using them.
Successful businesses integrate DLP policies into regular workflows.
Some practical examples include:
Reviewing High Risk files weekly.
Monitoring recurring risk patterns.
Investigating unusual increases in risk activity.
Providing additional guidance when trends emerge.
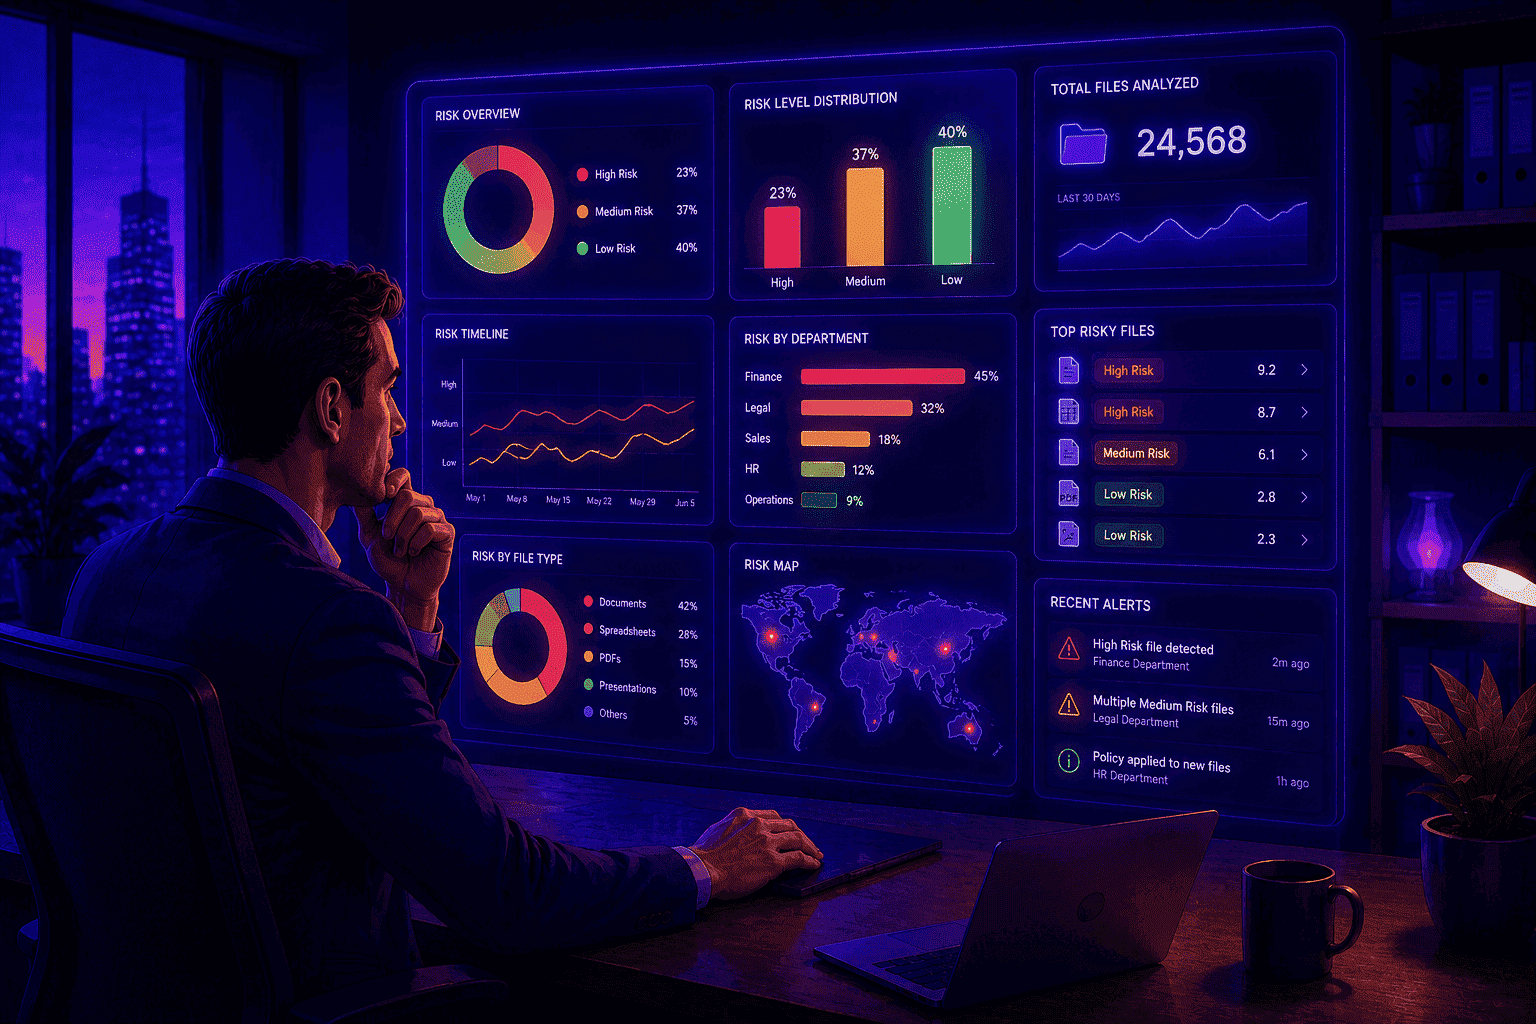
This is where DLP dashboards become valuable.
OrbityTrack's DLP dashboards and timelines allow managers to see how risk evolves over time, helping them determine whether policies are reducing risk or whether adjustments are needed.
Visibility transforms policies from static documents into active management tools.
Measuring Whether Your Policies Are Working
Many companies create DLP policies but never evaluate their effectiveness.
A good policy should produce measurable results.
Organizations should periodically ask:
Are High Risk incidents decreasing?
Are recurring issues being resolved?
Are employees handling sensitive information more consistently?
Are investigations becoming faster?
The answers often reveal whether policies are driving meaningful improvements.
One of the most overlooked aspects of DLP management is trend analysis. A single incident may not be significant, but repeated incidents often indicate process weaknesses that require attention.
The strongest DLP programs use data not only to identify risks but also to improve policies over time.
Continuous refinement helps organizations stay aligned with changing business processes while maintaining practical and effective protection.
Quick Takeaways
DLP policies define how sensitive information should be handled.
Simple policies are often more effective than complex ones.
Risk-based approaches help prioritize investigations.
Employee awareness is just as important as technology.
AI can simplify policy enforcement and risk detection.
DLP dashboards provide visibility into policy effectiveness.
Good policies focus on prevention rather than punishment.
Conclusion
DLP policies are not about creating more rules. They are about creating clarity.
Organizations that define how sensitive information should be handled are better positioned to reduce risk, improve consistency, and respond more effectively when issues arise.
Modern DLP solutions simplify this process by providing risk-based visibility through AI-powered analysis, risk classification, and trend monitoring.
The most effective policies are usually the simplest ones: clear expectations, practical processes, and consistent review. When combined with the right visibility tools, they become a powerful foundation for protecting sensitive information.


Try OrbityTrack for 7 Days!
Boost Productivity.
Turn data into results.
Gain full visibility over your team.
Start Your Free Trial