DLP Incident Response: Acting Before Data Loss Spreads
Lauren Mitchell
Introduction
Detecting a risky file is important. Responding effectively is even more important.
Many organizations invest in security tools that generate alerts, but alerts alone do not reduce risk. What protects a business is the ability to identify potential issues quickly, understand their severity, and take appropriate action before sensitive information is exposed.
This is where a strong DLP incident response process becomes essential. Whether the risk involves customer information, financial records, internal reports, or confidential business documents, organizations need a clear way to prioritize and investigate incidents.
Modern DLP platforms are increasingly moving away from complex rule management and focusing instead on visibility, risk analysis, and faster decision-making. In this article, we'll explore what DLP incident response means, why it matters, and how businesses can build a practical process that helps reduce data loss risk without creating unnecessary complexity.
Why DLP Incident Response Matters
Many companies assume that identifying sensitive files is enough.
In reality, detection is only the first step. The real challenge begins after a potentially risky file has been identified.
Without a response process, organizations often face several problems:
Too many alerts
Unclear priorities
Delayed investigations
Inconsistent decision-making
As businesses grow, the volume of files being created and shared increases significantly. Security teams and managers cannot manually review every document.
That is why incident response must focus on prioritization.
A High Risk file containing customer information deserves more attention than a Low Risk document with limited exposure potential.
The objective is not to investigate everything equally. The objective is to quickly identify what matters most and allocate resources accordingly.
Organizations that respond efficiently can reduce risk exposure while minimizing operational disruption.
Building a Practical DLP Response Process
Many businesses make incident response more complicated than necessary.
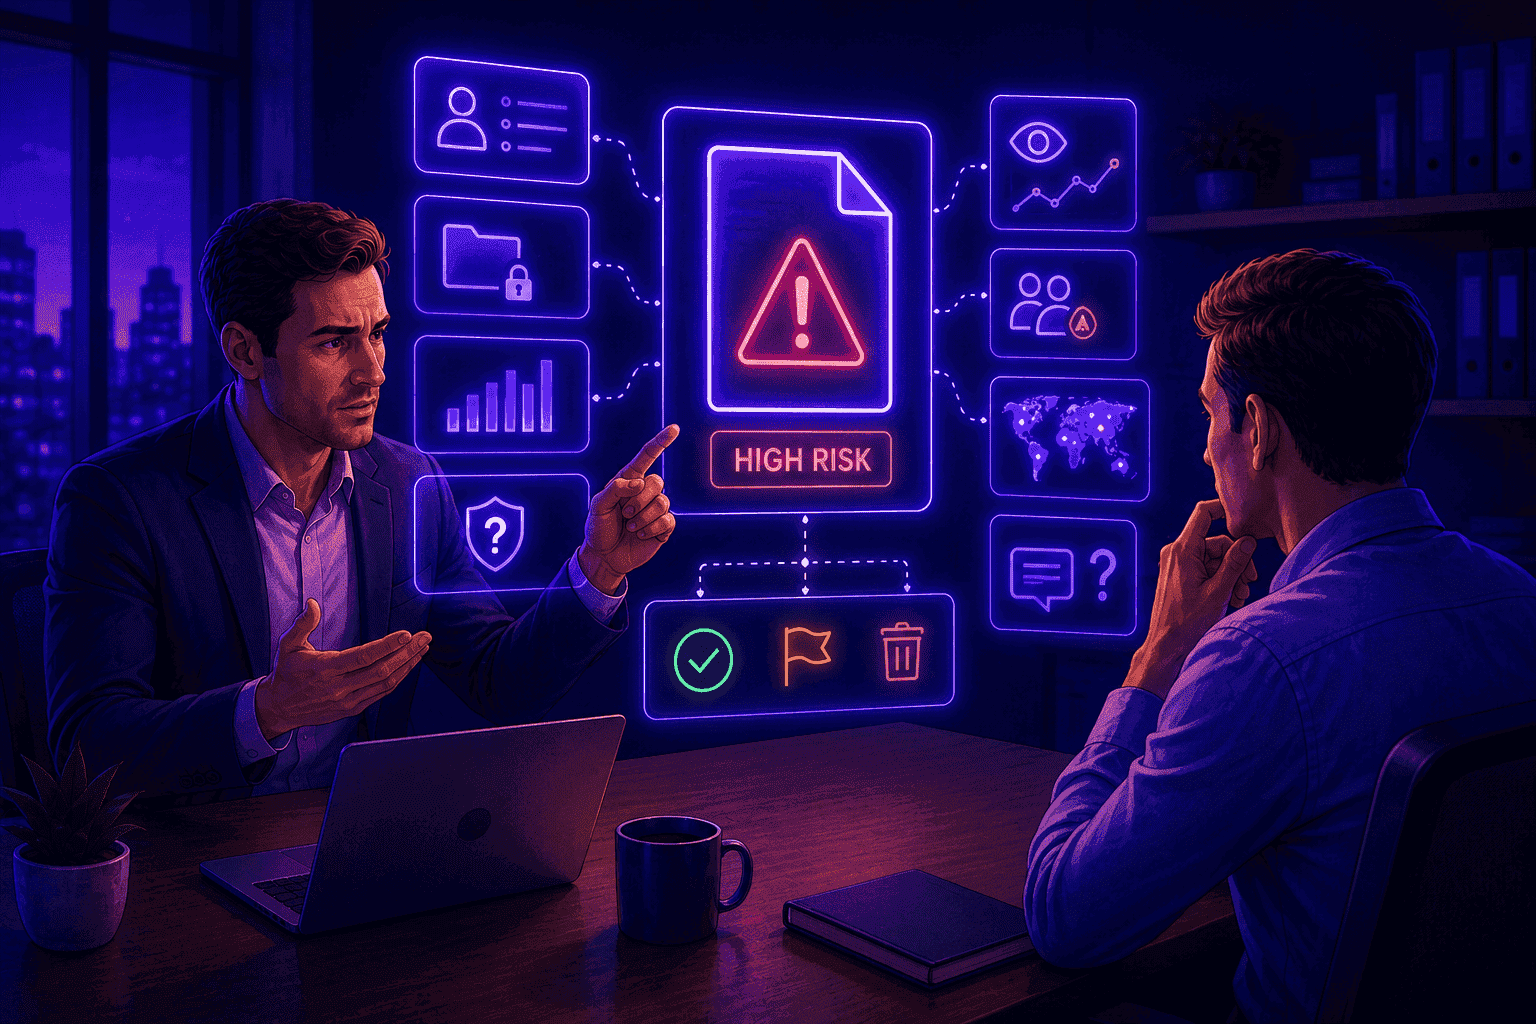
A practical DLP process can often be reduced to four simple stages:
Detection
The system identifies files that may contain sensitive information.
Risk Evaluation
Files receive a Risk Index and Risk Range that help determine severity.
Investigation
Managers or responsible teams review the file and understand why it was classified as risky.
Decision
The organization determines whether action is required.
This approach works particularly well for business teams because it avoids overwhelming users with technical security concepts.
For example, modern AI-powered DLP systems can automatically classify files into Low, Medium, or High Risk categories while providing a justification for the classification.
Instead of asking managers to interpret dozens of technical alerts, the system helps them focus on the files that deserve immediate attention.
The simpler the workflow, the more likely it is to be followed consistently.
Using Risk Classification to Prioritize Incidents
One of the biggest challenges in DLP incident response is determining where to start.
Not all incidents represent the same level of risk.
This is why risk-based classification has become increasingly valuable.
Platforms such as OrbityTrack's DLP solution automatically evaluate file content and assign:
Risk Index
Risk Range
AI-generated justification
This provides immediate context.
A High Risk file might contain confidential customer information, financial records, credentials, or other highly sensitive content.
A Medium Risk file may require attention but not immediate escalation.
A Low Risk file can often be reviewed later without creating unnecessary urgency.
By organizing incidents according to risk, managers spend less time sorting through alerts and more time addressing genuine concerns.
This significantly improves response efficiency while reducing alert fatigue.
Using Dashboards and Timelines for Faster Response
Responding to individual incidents is important, but understanding broader trends is equally valuable.
A single risky file may be an isolated event.
Repeated incidents across multiple days or multiple employees may indicate a larger process problem.
This is where visual analytics become useful.
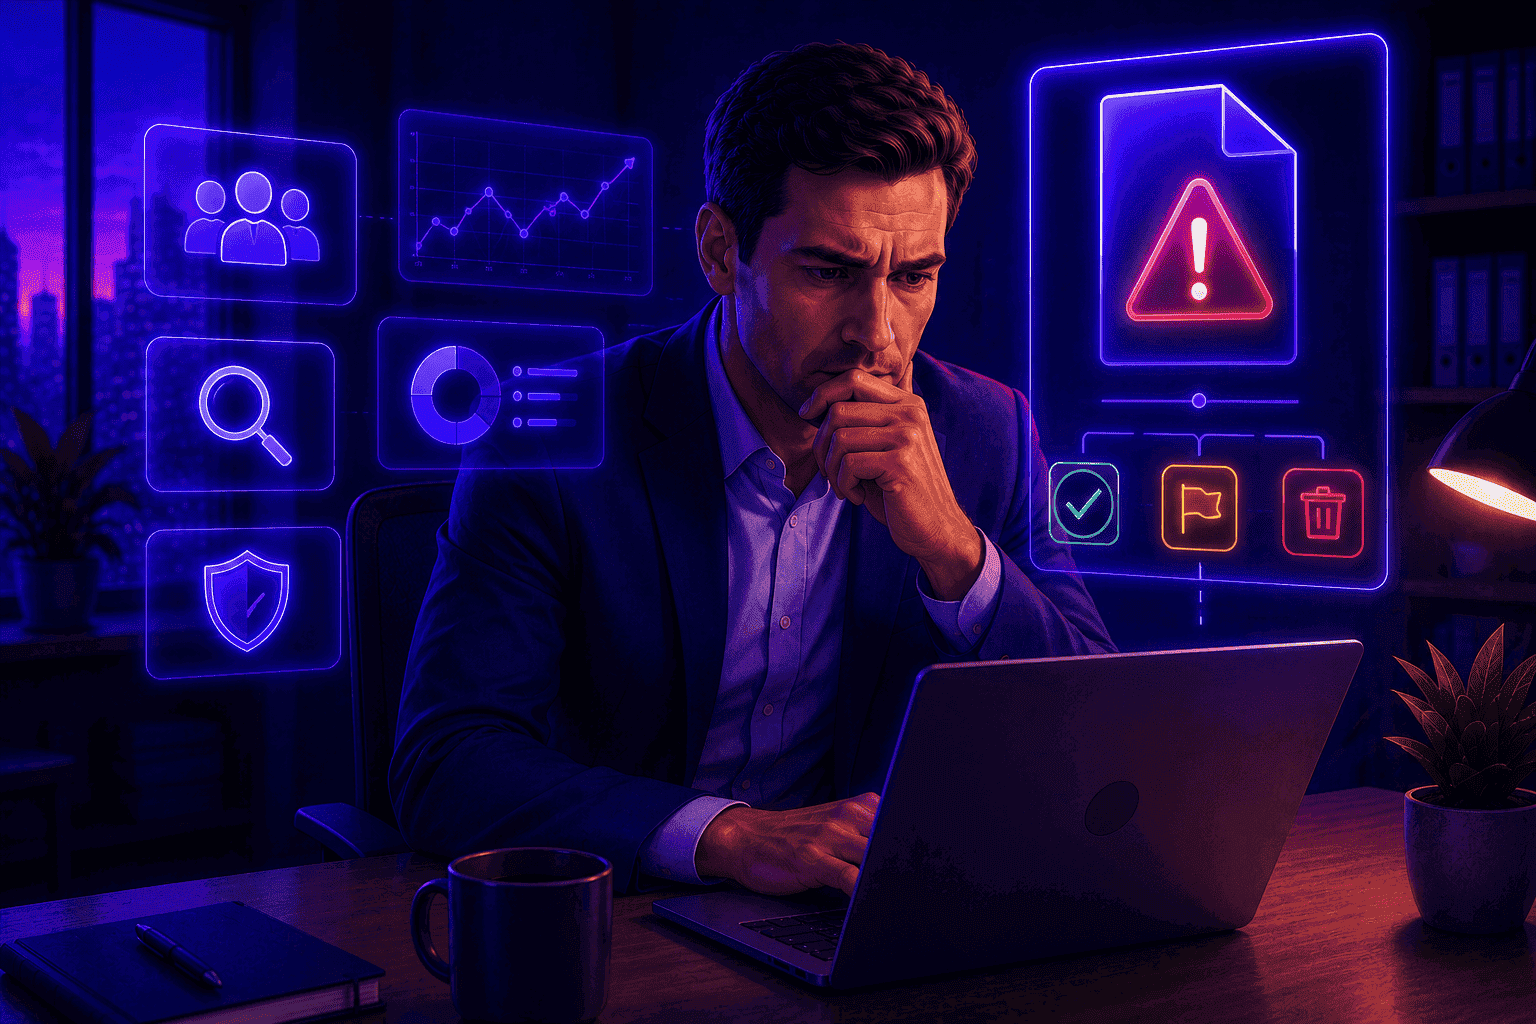
Modern DLP dashboards help organizations identify:
Risk trends over time
Members generating the most incidents
High-risk periods
Changes in organizational risk levels
OrbityTrack's DLP timeline and risk dashboards provide this type of visibility by showing when files were detected, how risk evolved, and where attention should be focused.
Rather than reacting to isolated events, leaders can identify patterns and take preventive action.
In many cases, the biggest value comes not from solving one incident, but from discovering the process that keeps creating similar incidents.
Turning Incident Response Into Continuous Improvement
The most effective DLP programs treat incident response as a learning process.
Every incident provides information.
A repeated pattern may indicate a training gap.
A particular department may require better handling procedures.
Certain document types may need additional controls.
Organizations that review incident trends regularly can improve security without creating friction for employees.
The goal is not to punish mistakes.
The goal is to understand why risks occur and reduce the likelihood of future incidents.
When DLP is approached from this perspective, it becomes a business improvement tool rather than simply a security system.
Over time, organizations gain better visibility, faster response times, and a stronger understanding of how sensitive information moves throughout the business.
Quick Takeaways
DLP incident response starts with visibility, not just alerts.
Risk prioritization helps teams focus on the most important incidents.
AI can improve incident classification and investigation speed.
Historical trends often reveal larger security problems.
Fast response reduces the impact of potential data exposure.
Simpler processes are often more effective than complex workflows.
Dashboards and timelines improve risk awareness across teams.
Conclusion
Effective DLP incident response is not about generating more alerts. It is about creating a clear process for understanding and managing risk.
Organizations that prioritize visibility, risk classification, and trend analysis can respond faster and make better decisions.
Modern AI-powered DLP solutions help simplify this process by automatically evaluating files, assigning risk levels, and highlighting the incidents that deserve immediate attention.
As businesses continue handling larger volumes of sensitive information, a practical incident response strategy will become an essential part of reducing data loss risk and improving operational awareness.


Try OrbityTrack for 7 Days!
Boost Productivity.
Turn data into results.
Gain full visibility over your team.
Start Your Free Trial